Blogs

Microsoft Purview vs Defender vs Sentinel: What’s the Difference?
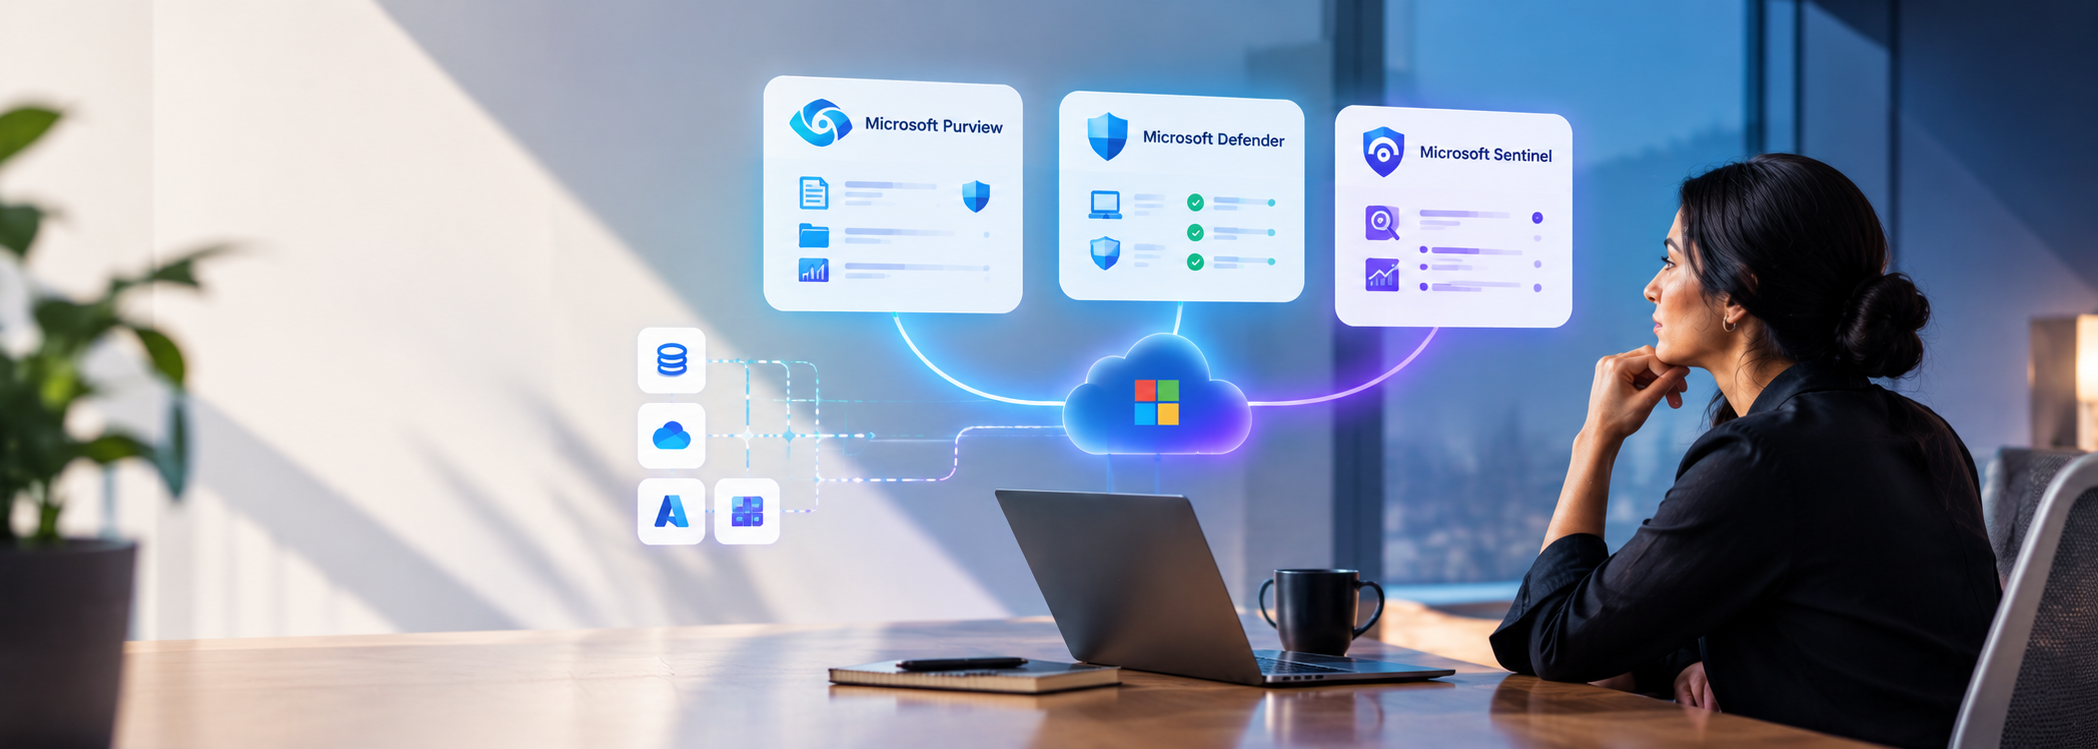
Three Microsoft Security Solutions, Three Different Roles

Microsoft Purview, Microsoft Defender, and Microsoft Sentinel are three names that frequently appear together when organisations discuss Microsoft security. But they do not solve the same problem.

That can make it difficult for IT leaders and business decision-makers to understand where each platform fits.

– Is Microsoft Purview an endpoint security tool?
– Is Microsoft Defender a SIEM?
– Do you need Microsoft Sentinel if you already have Microsoft Defender?
– And where does data protection fit into the overall security strategy?

The simplest way to understand the difference is this: Microsoft Purview focuses on your data. Microsoft Defender focuses on threats and attacks. Microsoft Sentinel focuses on security monitoring, investigation, and response across your wider environment.

These platforms can work together, rather than being alternatives to one another. Microsoft specifically describes Defender XDR and Sentinel as complementary technologies, with Defender providing extended detection and response and Sentinel providing SIEM capabilities.

Understanding these differences can help organisations build a more structured Microsoft security environment and avoid treating every security challenge as the same problem.

Microsoft Purview: Protecting and Governing Your Data

Think about the information your organisation handles every day.

– Customer Information

– Financial Records

– Contracts

– Employee Information 

– Business reports

– Intellectual property

– Emails and documents

The first security question is not necessarily, “Is someone attacking us?”

It can be: “What sensitive data do we have, where is it located, and who should be able to access or share it?”

This is where Microsoft Purview comes into the picture.

Microsoft Purview provides data security and information protection capabilities that help organisations discover, classify, protect, and govern sensitive information across different environments.

What does Microsoft Purview do?

Purview can help organisations understand their data and apply appropriate controls around it.

For example, an organisation may have sensitive information stored across:

– Microsoft SharePoint

– OneDrive

– Microsoft Teams

– Exchange Online

– End-user devices

– Cloud applications

– Other data sources

Without appropriate classification and protection, sensitive information can easily be copied, shared, downloaded, or sent to the wrong person.

Purview provides capabilities such as sensitivity labels, Data Loss Prevention (DLP), information protection, data security posture management, and insider risk management to help organisations address these challenges.

For example, sensitivity labels can help identify information based on its level of sensitivity and apply protection policies accordingly.

DLP can help organisations identify and control activities involving sensitive information.

This makes Purview particularly relevant when the business question is: “How do we protect our information and control how sensitive data is used?”

A simple way to think about Purview

Data → Discover → Classify → Protect → Govern

Purview is therefore less about identifying whether a laptop has malware and more about understanding and protecting the information that matters to the business.

Microsoft Defender: Protecting Against Threats

Now consider a different scenario. An employee receives a suspicious email. They click a malicious link. Their credentials are compromised. The attacker attempts to access another application. Suspicious activity begins appearing across the environment. This is where Microsoft Defender becomes important.

Microsoft Defender XDR is designed to provide extended detection and response across areas such as endpoints, email, applications, and identities. It automatically collects, correlates, and analyses security signals to help security teams detect and respond to threats.

Instead of looking at every security alert separately, Defender XDR can connect related signals and provide a broader view of an incident.

What does Microsoft Defender protect?

What does Microsoft Defender protect

The Defender ecosystem includes different security capabilities for different parts of the environment.

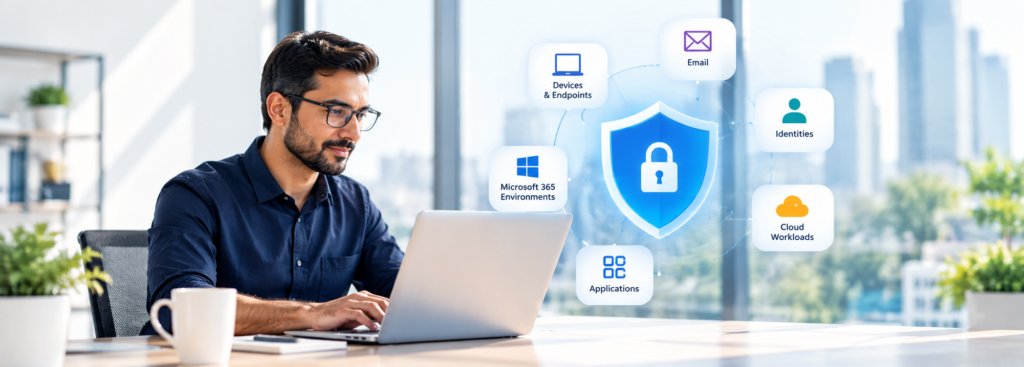
Depending on the Microsoft Defender services deployed and licensed in the environment, protection can extend across:

– Endpoints and devices

– Email

– Identities

– Cloud applications

– Microsoft 365 environments

– Cloud workloads

For example, Microsoft Defender for Endpoint focuses on endpoint security, while Microsoft Defender XDR brings signals from multiple security domains together.

The objective is to move beyond simply detecting individual alerts. Instead, security teams can investigate how different signals may be connected.

Why does this matter?

Imagine an organisation receives five separate alerts:

– A suspicious login

– An unusual email

– A potentially compromised endpoint

– A suspicious PowerShell activity

– An attempt to access a business application

Looking at these individually could make them appear unrelated. But when they are correlated, they may represent different stages of the same attack. That broader context is one of the key ideas behind Extended Detection and Response, or XDR.

Microsoft describes Defender XDR as an XDR solution that correlates security signals across Microsoft 365 services and can help security teams investigate and respond to threats.

A simple way to think about Defender

Threat → Detection → Investigation → Response

If the question is: “Are our users, devices, applications, or identities being targeted by a threat?”

Microsoft Defender is a major part of the answer.

Microsoft Sentinel: Seeing the Bigger Security Picture

Now imagine that your organisation has more than just Microsoft 365.

Perhaps you also use:

– Azure

– Firewalls

– Network appliances

– Business applications

– Third-party cloud platforms

– SaaS applications

– Infrastructure from different vendors

– Security tools from multiple providers

Your security team now has information coming from many different places.

This creates another challenge: How do you bring those signals together and understand what is actually happening across the environment?

This is where Microsoft Sentinel fits.

Microsoft Sentinel is Microsoft’s cloud-native Security Information and Event Management (SIEM) platform. It can collect security information from different sources, correlate signals, support investigation, and help organisations respond to threats. It also supports multicloud and multiplatform environments.

Microsoft Sentinel is also transitioning fully to the Microsoft Defender portal, with the Azure portal experience scheduled to retire on 31 March 2027. Organisations still managing Sentinel through the Azure portal should plan their migration to ensure a smooth transition.

How Microsoft Purview, Defender and Sentinel Work Together

This is where the conversation becomes more interesting.

A modern security strategy is rarely about deploying one tool and expecting it to solve every security problem.

Instead, different security capabilities can work together.

Consider a simple example.

Step 1: Sensitive information is identified

An organisation uses Microsoft Purview to identify and classify sensitive information.

For example, certain documents may contain financial or personal information.

Policies can then be applied to help protect that information.

Step 2: A suspicious activity occurs

An employee’s credentials are compromised.

The attacker attempts to access business resources.

Microsoft Defender can detect suspicious activity across relevant identities, endpoints, email, and applications.

Step 3: Security signals are correlated

Other suspicious activity is detected in the environment.

Microsoft Sentinel can collect security data from Microsoft and non-Microsoft sources, helping security teams monitor and investigate activity across the wider environment. In the Microsoft Defender portal, Sentinel is integrated into a unified security operations experience, where Sentinel and Defender capabilities work together through shared incident management.

When Microsoft Sentinel is onboarded to the Defender portal, its incidents are managed through the Defender portal’s unified incident experience. Alerts from Sentinel can be correlated with Defender signals, allowing related activity to be together for investigation.

The result is a more connected security approach:

Purview → Discover, classify, protect and govern data
Defender → Detect, investigate and respond to threats
Sentinel → Collect, analyse and orchestrate security operations across the environment

This is why organisations should not necessarily ask, “Which one should we choose?”

A more useful question can be: “Which security problems do we need to address, and how should these capabilities work together?”

A Real-World Example

Consider a company with 500 employees using Microsoft 365, Azure, laptops, SaaS applications, and a mixture of cloud and on-premises systems.

The company has three different challenges.

Challenge 1: Sensitive documents are being shared externally

Employees regularly share documents through Teams, SharePoint and email.

The IT team is concerned about sensitive business information leaving the organisation.

This is primarily a data security and information protection challenge.

Microsoft Purview can be relevant here.

The organisation can use capabilities such as classification, sensitivity labels and DLP policies to help identify and protect sensitive information.

Challenge 2: Employees are receiving sophisticated phishing emails

One employee clicks a malicious link.

An endpoint begins showing suspicious behaviour.

The user’s identity also shows unusual activity.

This becomes a threat detection and response challenge.

Microsoft Defender XDR can bring together signals from relevant security services and help security teams investigate the incident.

Challenge 3: Security information is spread across multiple platforms

The organisation also has firewall logs, Azure activity, third-party applications and other infrastructure generating security events.

The security team needs a centralised way to analyse these signals.

This is where Microsoft Sentinel can provide SIEM capabilities and broader security visibility.

The three technologies therefore address different parts of the same overall security strategy.

Why the Difference Matters for IT Leaders

For IT leaders, understanding these distinctions is not just about knowing Microsoft’s product portfolio.

It is about making sure security investments address actual business risks.

An organisation may have strong endpoint protection but limited visibility into sensitive data.

Another may have good data classification but limited centralised security monitoring.

Another may have multiple security tools but no effective way to correlate the information they generate.

Security maturity is therefore not simply about having more tools.

It is about whether the tools work together to address the organisation’s actual risks.

Microsoft’s guidance highlights the complementary relationship between Defender XDR and Sentinel, including their integration for unified security operations.

The same principle applies when considering data protection.

Security teams need visibility into both what attackers are doing and what information they could potentially access or compromise.

Final Thoughts

Microsoft Purview vs Microsoft Defender vs Microsoft Sentinel - Key differences

Microsoft Purview, Microsoft Defender and Microsoft Sentinel are often discussed together because they can contribute to a connected Microsoft security environment. But their primary purposes are different.

Purview is centred around data security and information protection.

Defender is centred around threat detection, investigation and response.

Sentinel is centred around SIEM capabilities and broader security monitoring.

The goal should not simply be to deploy all three because they are available within the Microsoft ecosystem. Instead, organisations should first understand their security priorities and then determine where each technology fits.

Mismo Systems is a Microsoft Solutions Partner for Security, helping organisations strengthen their security posture across Microsoft 365, cloud, identity, endpoints, and data. With expertise across Microsoft Purview, Microsoft Defender, Microsoft Sentinel, Entra ID, Intune, and Microsoft 365 security, we help businesses build practical and connected security environments aligned with their needs.

For some organisations, the immediate priority may be understanding and protecting sensitive data.

For others, it may be strengthening endpoint and identity threat protection.

For organisations with complex environments, centralised security monitoring and SIEM capabilities may be a major requirement.

And in many environments, these needs overlap. That is where the combination becomes valuable.

Purview helps answer: “What data are we protecting?”

Defender helps answer: “What threats are we facing?”

Sentinel helps answer: “What is happening across our security environment?”

Understanding these three questions is a useful starting point for building a more structured, connected and business-focused Microsoft security strategy.

If you’re unsure where to start, request a Free Microsoft 365 Security Assessment or Contact Our Security Experts

FAQs

Microsoft Purview focuses on data security, information protection, governance, and compliance. Microsoft Defender focuses on detecting, investigating, and responding to threats across endpoints, identities, email, and applications. Microsoft Sentinel is a cloud-native SIEM that provides broader security monitoring, correlation, investigation, and response across an organisation’s environment.

Yes. These solutions address different areas of security and can work together as part of a broader Microsoft security strategy. Purview helps protect sensitive data, Defender helps detect and respond to threats, while Sentinel can bring security signals together for broader monitoring and investigation.

No. Microsoft Sentinel is primarily a SIEM platform designed for security monitoring and analysis across different environments. Microsoft Defender XDR focuses on extended detection and response across areas such as endpoints, identities, email, and applications. They can be integrated to support a more connected security operations approach.

Microsoft Purview is particularly relevant when an organisation needs better visibility and control over sensitive information. Common use cases include data discovery and classification, sensitivity labels, Data Loss Prevention (DLP), information protection, and compliance requirements.

Not necessarily. The right combination depends on the organisation’s security requirements, existing Microsoft environment, risks, compliance needs, and security maturity. Organisations should first identify their key security challenges and then determine which capabilities are required to address them.

No Comments

Comments On "Microsoft Purview vs Defender vs Sentinel: What’s the Difference?"

Leave a Reply

Your email address will not be published. Required fields are marked *

Recent Blogs

Oct

15

2026

Microsoft Purview vs Defender vs Sentinel: What’s the Difference?
Three Microsoft Security Solutions, Three Different Roles Microsoft Purview, Microsoft Defender, and Microsoft Sentinel are three names that frequently appear
Sept

25

2026

10 Business Questions Every Leader Should Ask Cazper

The Problem Isn’t Data. It’s Getting Answers. Business leaders rarely lack data. The problem is getting a clear answer from
Sept

23

2026

How Travel Analytics Is Shaping the Future of Tourism

The Data Revolution Behind Every Journey Travel businesses generate data at almost every stage of the customer and operational journey.
Aug

25

2026

Is Your Microsoft 365 Environment Secure? 5 Things IT Heads Need to Check

Microsoft 365 Isn’t Secure by Default Microsoft 365 is one of the most widely used cloud productivity platforms, but being
July

23

2026

Introducing Cazper: An AI-Powered Business Intelligence Assistant from Mismo Systems

Why Every Business Needs an AI-Powered Business Intelligence Assistant Businesses today generate more data than ever before. From sales and
May

01

2025

From Data to Decisions: How Data Analytics is Transforming UK Enterprises

Introduction Imagine knowing what your customers want before they even realize it. What if you could anticipate market trends, optimize
Apr

29

2025

Effective Multi-Cloud Management: Security, Cost Optimization, and Strategy

Mastering Multi-Cloud Management in 2025: Centralization, Security, Cost, and Automation Introduction The multi-cloud management platform market reached $13.33 billion in
Apr

09

2025

Power BI in 2025: Latest Features, Trends & Best Practices

Introduction In the fast-changing business intelligence landscape, data is much more than simple digits—it lays the cornerstone for tactical choices.
Mar

21

2025

Azure Landing Zones: Build Secure, Scalable Cloud Foundations

Want to build a secure, scalable cloud setup? Discover how Azure Landing Zones create a strong foundation for your cloud
Mar

13

2025

Advance Analytics with Microsoft Fabric

Unlock the full potential of Microsoft Fabric and take your analytics game to the next level! In this exclusive webinar,
Feb

24

2025

How to Migrate VMware to Azure? Plan, Execute and Optimize Your Migration using Azure.

For several years, VMware solutions have been at the forefront of the business world, trusted as the virtualization platform powering
Feb

17

2025

Microsoft Fabric Architecture Guide 2025 – Key Insights & Features

Microsoft Fabric is an integrated analytics and data platform designed to meet the needs of large enterprises. It combines various
Jan

27

2025

Ensuring Optimal Active Directory Health, Security, Performance, and Upgrades

Active Directory Domain Service (AD DS) is widely used directory service and foundation of Windows domain network in organizations. It
Jan

20

2025

Transform Your Business with Power Automate, Power Apps, and Copilot Studio

Microsoft’s Power Platform is a robust suite of tools designed to empower businesses to innovate and transform their operations. It
Jan

09

2025

How to Manually Migrate a WordPress Website from One Host to Another

Migrating a WordPress website from one host to another can seem daunting, but with a step-by-step guide, the process becomes
Dec

18

2024

A Stress-Free Guide to Setting Up Your Azure Environment

It’s like going on an adventure when you start your cloud journey. It may make you happy, but if you’re
Dec

18

2024

Microsoft Fabric Uncovered Capabilities Advantages

In this blog we will dive into Microsoft Fabric and go over the core services offered on the Fabric platform.
Nov

18

2024

MS Fabric and the Future of Predictive Analytics: What to Expect

Uncover how MS Fabric is transforming predictive analytics and what innovations lie ahead for businesses and technology.
Nov

12

2024

Unlock the Power of AI with Microsoft Copilot Studio

In this webinar, we dive deep into Microsoft’s transformative AI technology and show you how to create custom AI assistants
Nov

07

2024

Power BI for Business Success: Making Data-Driven Decisions Easy

Learn how to make the most of Power BI’s sharing functionalities to drive impactful data-driven decisions.
Nov

07

2024

Setting up High Availability and Disaster Recovery for Enterprise Applications

Learn how to ensure business continuity, minimize downtime, and protect your critical systems with best practices for HA and DR.
Nov

07

2024

Analytics Unplugged: From Raw Data to Actionable Insights

Dive into the world of Data Analytics and discover how to harness the power of data for smarter decisions and
Nov

07

2024

Overcoming Cloud Migration Challenges

Cloud migration offers numerous benefits, but it also comes with its own fair share of challenges Delve into the most
Oct

18

2024

Rescuing Important Emails from the Junk Folder with Microsoft Graph API

Introduction: Because, Of Course, It Had to Be the CEO Let me paint you a picture: we were managing the
Oct

07

2024

Cloud Adoption Challenges

Tune in for a deep dive into overcoming hurdles in cloud adoption using real-world solutions from our co-founder, Vineet Arora.
Sept

17

2024

Power BI Consulting Company

Power BI Consulting Company: Empowering Businesses with Data-Driven Insights In today’s competitive landscape, organizations need actionable insights to stay ahead.
Sept

17

2024

Power BI Partners

Power BI Partners: Driving Data-Driven Solutions As a trusted Power BI partner, Mismo Systems is dedicated to empowering organizations with
Sept

17

2024

Power BI Development Company

Empowering Data-Driven Insights in India (Delhi, Noida, Bangalore) and USA In today’s digital landscape, businesses are generating vast amounts of
Sept

17

2024

Power Bi Development Services

Power BI Development Services: Unlocking Data-Driven Success At Mismo Systems, we offer specialized Power BI development services to help organizations
Sept

10

2024

Power BI Service for Enterprise Analytics

In today’s data-driven business landscape, enterprise analytics plays a crucial role in informed decision-making and maintaining a competitive edge. Microsoft’s
Sept

10

2024

Planning Your Legacy Application Migration to Containers

This blog post is in continuation to “Why Migrate Legacy Applications to Containers and What are the Challenges this Brings?”
Aug

05

2024

Azure AI, ML Studio & OpenAI: Simplifying Microsoft’s AI Ecosystem

In today’s rapidly evolving technological landscape, integrating artificial intelligence (AI) and machine learning (ML) into business operations is no longer
Aug

05

2024

Why Migrate Legacy Applications to Containers and What are the Challenges this Brings?

Introduction to Containerization Containerization is the era to welcome: a time where complexity would confront simplicity in the field of
Apr

18

2024

Azure Log Analytics Workspace – Ensuring Compliance, Centralizing and Streamlining Monitoring

In the realm of cloud computing, the ability to monitor, analyze, and respond to IT environment anomalies is crucial for
Apr

17

2024

Azure Stack HCI 3-node Cluster Configuration – Switchless Storage Network

Mismo Systems implemented a 3-node Azure Stack HCI cluster for one of the clients. The cluster was configured with a
Oct

04

2023

Microsoft update: Chat with users with Teams personal accounts

Chat with Teams will extend collaboration support by enabling Teams users to chat with team members outside their work network
Dec

01

2022

AWS vs Azure

The cloud service providers AWS and Azure are truly miraculous helping millions across the globe creating a virtual space with
Apr

25

2022

The need for a hybrid solution – Azure Stack HCI

Microsoft’s Azure Stack HCI is a hyper-converged infrastructure with virtualization, software-defined networking, and more. What separates it from the rest

Jan

10

2022

Azure Virtual Desktop vs Windows 365

Azure Virtual Desktop (AVD) is a Desktop as a Service (DaaS) solution offered on Microsoft Azure, previously named Windows Virtual
Nov

16

2021

Microsoft 365 Update:- Viva Connections is now generally available!

Viva Connections, part of Microsoft Viva, is your entry point to a modern employee experience. You get an all-in-one experience with the customized
Nov

16

2021

Microsoft 365 Update:- Meeting Activities in Teams Audit Log

Meeting Activities have been added to the Microsoft Teams audit log to help organizations respond more effectively to security events, forensic investigations,
Nov

15

2021

Azure Update:- Global Disaster Recovery via Azure Site Recovery

Azure Site Recovery is a Cloud-driven, highly innovative, and automated disaster recovery solution (DRaaS). Azure’s native platform capabilities for high
Nov

15

2021

Azure Update:- Screen Capture Protection for Azure Virtual Desktop

Azure Virtual Desktop is a service running in the cloud that enables your users to access the data, applications, and
Nov

15

2021

Azure Update:- Immutable Storage with versioning for Blob storage

Azure blob storage is massively scalable and secure object storage for cloud-native workloads, archives, data lakes, high-performance computing and machine
Nov

10

2021

How is Cloud transforming Industries?

Cloud technology has been impactful in transforming business. From cost savings to easy collaboration, the usage of the Cloud has
Sept

27

2021

4 Tips for Protection Against Unsafe Emails

Earlier, the spotting of malicious content in emails was quite an easy task. However, due to the rise in technology,
Sept

24

2021

How is hybrid cloud useful for midsize/large businesses?

A hybrid cloud can be defined as a cloud computing environment that utilizes a combination of on-premises private cloud and
Sept

22

2021

How to Protect Your Data from a Ransomware Attack

What is a Ransomware attack? It can be defined as a malware attack that is carried out deliberately to encrypt
Aug

24

2021

Build superpower apps, with no code-Power apps

PowerApps is a tool that allows you to create custom apps, leveraging many of the features of the Office 365
Aug

11

2021

Why do you need a Modern Workplace – M365?

Microsoft 365, a world of enhanced productivity and collaboration that drives a team to achieve more together, is a complete
July

02

2021

Microsoft Teams Updates (June 2021)

In this blog, we will be discussing the various Microsoft Teams updates in the month of June. Meeting Updates: During
June

22

2021

Microsoft rebrands Windows Virtual Desktop as Azure Virtual Desktop

Microsoft’s virtual desktop infrastructure platform has been rebranded under the Azure name and notified of new security and management capabilities
May

07

2021

How Startups can succeed with Cloud Computing?

Startups are an enjoyable but demanding professional experience. A host of entrepreneurially dedicated professionals pursue their passion and dive into
May

04

2021

Azure AD SSO & AWS – Connecting the Rivals

Being part of Mismo Systems, I am fortunate enough to get to work on a diverse set of projects. Few

May

04

2021

A quick look at the 4 Most Used Services on Microsoft Azure

1. Azure Compute Azure compute is an on-demand computing service for running cloud-based applications. Azure compute service can be divided broadly into three
May

01

2021

Cloud Security – A shared responsibility

We see all businesses small or big, consuming cloud technology in one or another way. The pandemic has increased the

Apr

18

2021

Breakout Rooms and Its Usage – Microsoft Teams

In this blog, we are going to discuss a feature provided by Microsoft teams known as Breakout rooms. Also, we

Apr

12

2021

Is Cloud cheaper than On-premises Data Centres?

Cloud has bloomed over the last decade, according to Goldman’s analysts almost 23% of IT workloads now live on Public

Apr

04

2021

Hosting with Transparency, Compliance, and Security

We help customers host applications on the cloud, this includes accounting systems including Tally, ERP software including SAP, and Navision.
Apr

04

2021

Future of Cloud Computing

Cloud computing has established itself as the inevitable future when it comes to IT services. This picture becomes much clearer

Apr

04

2021

AWS Security Features

The Amazon Web Services (AWS) in terms of security follow a shared responsibility model. So, the security ‘of’ the cloud is on

Mar

14

2021

Azure vs AWS

It’s Azure vs AWS!! Read this blog to know the major differences between Azure & AWS. What is Azure? Microsoft

Mar

04

2021

What is Budget in Azure and how can you set the Budget?

Budget in Azure to manage and monitor the spending or consumed cost for Azure services. We can apply budget on
Feb

09

2021

Azure Firewall

Azure Firewall is a managed, cloud-based network security service that protects your Azure virtual network resources. You can centrally create,

Feb

03

2021

Package Manager for Microsoft Intune Administrators – Part 1

Deploying applications to end-user Windows machines has never been easier if you are a Microsoft Intune administrator. Earlier what used

Feb

02

2021

Major Cloud Concerns – Do corporate agents, cyber hackers, and governments have access to my data if it is in the cloud?

This is one of the major cloud concerns for many companies, but it is irrational. Your IT team manages access,

Jan

04

2021

How Global admin can give someone’s OneDrive access to another user?

Please follow the below steps to use this feature. Go to Admin Center https://admin.microsoft.com/ > User>Active Users> Search Name>Click on User Profile.
Dec

04

2020

Microsoft Secure Score

Microsoft Secure Score is a security analytics tool that provides better security configuration and security features. It applies a numerical
Dec

04

2020

Top 10 Elements of The Cloud

In this blog I will be talking about the Top 10 elements of Cloud. Virtual Network: Create a logically isolated section

Nov

03

2020

How Cloud Computing Can Improve Your Business?

Cloud computing provides users with access to files, applications, data, and services from their Internet-connected devices, such as smartphones, laptops,

Sept

04

2020

Visio Tabs in Microsoft Teams

Visio Tabs in Microsoft Teams allows team members in a dedicated space to access resources and information in a channel

Aug

04

2020

Cloud or On-prem? – All you need to know about moving to Office 365

Protection and uptime are usual for Office 365 in the cloud. Companies are generating data at an utterly impressive pace
Feb

09

2019

Remove Azure AAD Connect

Let’s see the steps to disable AD Sync, remove AAD connect and move to cloud-only administration. 1. Download Azure Active