Why Microsoft 365 Security Readiness Matters Before Enabling Copilot
Microsoft 365 Copilot can help employees summarise meetings, find information, draft documents and work across business data. For IT teams, however, enabling Copilot involves more than assigning licences and showing employees how to use it.
The bigger question is whether the organisation’s existing data and security controls are ready for AI.
Consider a common situation. An employee can access a SharePoint folder containing confidential financial reports because the folder was shared with a large group several years ago. The access was never reviewed because nobody considered it a major risk. When Copilot is introduced, the employee may be able to find and summarise information from those files through a simple prompt.
Copilot hasn’t necessarily bypassed security. It may be using information the employee was already permitted to access. The problem is that the original permissions were too broad.
This is why Microsoft recommends reviewing data access, addressing oversharing and establishing appropriate security and governance controls before deploying Copilot.
Organisations can start by reviewing their existing Microsoft 365 security and governance controls before expanding AI access.”
For IT Heads and CTOs, the priority is clear: make sure your Microsoft 365 environment is ready for AI before making AI available across the business.
What Does AI Readiness Mean for Microsoft 365 Security?
This article focuses on the security and governance aspects of Microsoft 365 Copilot readiness. Licensing and technical requirements also need to be checked as part of deployment planning.
AI readiness means having the right data, permissions, security controls and governance processes in place to use AI safely within the organisation.
For Microsoft 365 Copilot, this includes reviewing who can access business information, how sensitive data is protected, whether existing sharing arrangements are appropriate and how AI usage will be monitored.
Copilot works with information available to the user through supported Microsoft 365 services and respects existing permissions and applicable security controls. It doesn’t automatically correct outdated access rights, clean up old files or decide whether an employee should have access to a particular document.
That distinction matters.
An organisation may already have Microsoft 365, multi-factor authentication and endpoint protection in place and still have gaps in its data governance. For example, confidential
documents might be stored in broadly accessible SharePoint sites, or former project folders might remain available long after the project has ended.
These issues deserve attention before Copilot is introduced.
Microsoft’s guidance on building a secure and governed foundation for Copilot provides a useful starting point for this work.
5 Microsoft 365 Security Checks to Complete Before Enabling Copilot
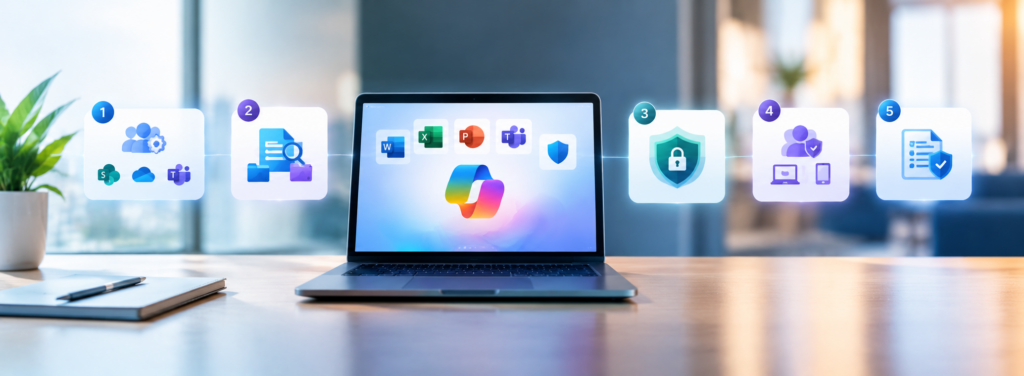
1. Review SharePoint, OneDrive and Teams Permissions
Start by understanding who can access the organisation’s information.
Over time, permissions can become difficult to manage. Employees move between departments, project groups change, external collaborators come and go, and old sharing links remain active. In some cases, access is granted to a much larger group than the business intended.
Before enabling Copilot, review:
– SharePoint sites and libraries with broad access permissions.
– OneDrive files and folders shared with colleagues or external users.
– Teams and Microsoft 365 groups with outdated membership.
– Anonymous or organisation-wide sharing links, where enabled.
– Sites with broken permission inheritance or unclear ownership.
– Access to confidential HR, finance, legal and customer information.
Pay particular attention to whether permissions still reflect how the business operates today.
For example, a finance
a finance folder may have been shared with an entire department when only a small group of employees needed access. Copilot makes information easier to discover, so correcting that permission before rollout is a sensible first step.
Microsoft provides guidance on preparing SharePoint for Copilot and identifying oversharing risks.
What IT leaders should ask: Can we confidently explain who has access to our sensitive business information, and why?
2. Identify Sensitive, Outdated and Unmanaged Data
Permissions are only part of the problem. Organisations also need to understand what information they hold and whether it is still needed.
A typical Microsoft 365 environment can contain years of accumulated documents, duplicate files, outdated policies, old project folders and content with no clear owner. Some of it may be harmless, while other material could contain personal information, financial records or confidential
business details.
Before a Copilot rollout, identify content that is:
– Sensitive but not adequately protected.
– Accessible to more users than necessary.
– Outdated, duplicated or no longer required.
– Stored in inactive or ownerless SharePoint sites.
– Missing a clear classification or retention approach.
The goal isn’t to delete everything old. Some records must be retained for legal, regulatory or business reasons. Instead, decide what should be retained, archived, restricted or removed according to the organisation’s policies.
Microsoft Purview and SharePoint Advanced Management offer capabilities that can help administrators assess data risks and identify sites requiring attention. Available features depend on the organisation’s licensing and configuration.
For further guidance, see Microsoft’s secure and governed data foundation for Copilot.
What IT leaders should ask: Do we know where our sensitive information lives, who owns it and how long it should remain accessible?
3. Put Data Protection Controls in Place
Once the organisation understands its data and permissions, the next step is
is to make sure sensitive information has appropriate protection.
Microsoft Purview can help organisations classify information, apply sensitivity labels, enforce Data Loss Prevention (DLP) policies and support compliance and auditing requirements.
For example, a business might classify financial forecasts as confidential and customer records as restricted. Appropriate policies can then help control how that information is shared and, where supported and configured, how Copilot can process it.
The important point is that purchasing Microsoft 365 Copilot does not replace the need for a data protection strategy.
IT teams should review:
– Whether sensitivity labels are defined and applied consistently.
– Whether DLP policies cover relevant sensitive information.
– Whether policies address applicable Copilot interactions and data sources.
– Whether retention, auditing and investigation requirements are understood.
– Whether the controls have been tested against real business scenarios.
Organisations should also check which capabilities are available under their current Microsoft 365 and Purview licences before designing the rollout.
Microsoft explains the available controls in its guide to security for Microsoft Copilot.
What IT leaders should ask: If an employee uses Copilot to work with sensitive information, do our existing policies provide the protection and oversight we need?
4. Check Identity, Access and Device Security
Copilot doesn’t operate separately from the organisation’s wider Microsoft 365 security environment. Its safe use depends in part on the identity, access and device controls already in place.
A strong starting point is to review Microsoft Entra ID, multi-factor authentication (MFA), Conditional Access and least-privilege access. IT teams should also check device compliance, endpoint protection and relevant threat detection controls.
The review should establish whether:
– MFA and appropriate authentication policies are enforced.
– Administrative privileges are limited to those who need them.
– Access policies reflect user, device and sign-in risk where appropriate.
– Managed devices meet the organisation’s security requirements.
– Microsoft Defender and other relevant security controls are configured and monitored.
Businesses looking to strengthen these controls can explore Mismo’s identity and access management solutions
The exact controls will vary by organisation, existing security maturity and licensing. A mid-market business doesn’t necessarily need to implement every advanced security feature before starting a pilot, but it should understand its gaps and prioritise the controls that protect its users and data.
Microsoft’s Zero Trust guidance for Microsoft 365 Copilot explains how identity, data protection, device security and access permissions fit into Copilot readiness.
What IT leaders should ask: Are our identity and access controls strong enough to protect the information Copilot can help employees find and use?
5. Establish Governance Before Expanding Copilot Access
Even with the right technical controls, organisations need clear rules for how Copilot will be introduced and used.
Employees should understand which business use cases are approved, what information requires extra care and when AI-generated content needs human review. IT teams need to know who is responsible for security decisions, policy management and investigating potential issues.
Ongoing support and reviews are also important after deployment. Learn more about Mismo’s Microsoft 365 managed services
A practical rollout should include:
– A defined business purpose and a small initial group of users.
– Clear guidance on acceptable AI use and sensitive information.
– Testing of permissions and protection controls before wider deployment.
– Appropriate audit logging, monitoring and incident response processes.
– Regular reviews of data exposure, access rights and policy effectiveness.
Start with use cases that provide genuine value without creating unnecessary risk. For example, summarising internal meetings or drafting routine business communications may be suitable pilot activities, provided the relevant data and permissions have been reviewed.
Use the pilot to identify problems, gather feedback and refine policies before extending access across departments.
Microsoft’s Copilot adoption guidance provides additional advice on preparing the tenant, selecting initial use cases and organising a rollout.
What IT leaders should ask: Do we have a clear plan to manage Copilot securely after the initial deployment, rather than treating readiness as a one-time exercise?
Microsoft 365 Copilot Readiness Checklist
Before enabling Copilot for a wider group of employees, IT teams can use the following checklist to review the essentials.
| Readiness Area | What to Check |
|---|---|
| Permissions | Review SharePoint, OneDrive and Teams access; remove unnecessary permissions and sharing links. |
| Data Governance | Identify sensitive, outdated, inactive and ownerless content. |
| Information Protection | Review sensitivity labels, DLP, retention and applicable compliance controls. |
| Identity and Devices | Validate MFA, Conditional Access, privileged access and device protection. |
| Governance and Monitoring | Define approved use cases, pilot users, audit requirements and ongoing reviews. |
This checklist is a starting point, not a guarantee of readiness. Organisations should validate controls against their own data, regulatory obligations, Microsoft 365 configuration and licensing.
Do You Need to Fix Everything Before Enabling Copilot?
Not necessarily. The objective is to identify and address the risks that could expose sensitive information or undermine the organisation’s security requirements.
A practical approach is to assess the current environment, prioritise high-risk content and permissions, apply temporary protections where appropriate, and remediate the underlying issues. The organisation can then validate the controls and expand the rollout in stages.
For example, a business might discover that several SharePoint sites contain sensitive information but are accessible to broad employee groups. Rather than enabling Copilot for everyone immediately, the IT team can review those sites, restrict access where needed and test the results before expanding deployment.
This approach allows organisations to make progress without overlooking security.
Microsoft’s secure and governed Copilot deployment guidance covers oversharing remediation, ongoing guardrails and regulatory considerations.
How Mismo Systems Can Help Prepare Your Microsoft 365 Environment
Preparing for Copilot is a useful opportunity to review the wider Microsoft 365 security environment, not just the AI deployment itself.
Mismo Systems helps organisations assess and strengthen their Microsoft 365 security, identity and data protection controls. This can include reviewing access permissions, identifying potential data exposure, evaluating Microsoft Purview capabilities and recommending practical improvements based on the organisation’s requirements.
For mid-market businesses, the objective is to establish a manageable security foundation that supports business productivity without losing sight of data protection and governance.
If your organisation is planning a Copilot rollout, start by understanding where your current environment stands and which gaps need attention.
Planning to enable Microsoft 365 Copilot? Review your security and data governance readiness before rolling it out across the business.
Final takeaway
Microsoft 365 Copilot can make everyday work easier, but the quality of the security and governance behind it matters. Reviewing permissions, protecting sensitive information and establishing clear controls before deployment helps organisations adopt AI with greater confidence.
FAQs
Microsoft 365 Copilot readiness means ensuring that an organisation’s data, access permissions, identity controls, information protection policies and governance processes are suitable for using Copilot securely. It also includes checking licensing, technical requirements and the organisation’s ability to monitor and manage the rollout.
Copilot can use information that a signed-in user is authorised to access. If SharePoint sites or files have overly broad permissions, Copilot may make that information easier for those users to find. Reviewing permissions helps reduce unintended exposure before deployment.
Not every organisation needs every Purview capability to begin using Copilot. However, Microsoft Purview provides important information protection, DLP, auditing and compliance capabilities that can support a secure deployment. The specific features available depend on licensing, configuration and business requirements.
Depending on the supported workload, licence and policy configuration, Microsoft Purview DLP and information protection controls can restrict Copilot’s use of certain sensitive content or interactions. Organisations should configure and test the relevant policies rather than assume that all sensitive data is automatically blocked.
One major risk is oversharing: employees may already have access to information that they should not need for their roles. Copilot can make this information easier to discover. Other considerations include sensitive data protection, identity security, compliance, user behaviour and ongoing monitoring.
Yes, provided it first assesses its risks and addresses the gaps that could create unacceptable exposure. A phased rollout can help an organisation prioritise high-risk permissions and data, validate essential controls and expand usage as its security and governance arrangements mature.
Start with data access and oversharing, particularly in SharePoint and OneDrive. Then review sensitive data protection, identity and device controls, compliance requirements and monitoring. These checks help IT teams identify the most important issues before assigning Copilot licences to a wider group of users.