Three Microsoft Security Solutions, Three Different Roles
Microsoft Purview, Microsoft Defender, and Microsoft Sentinel are three names that frequently appear together when organisations discuss Microsoft security. But they do not solve the same problem.
That can make it difficult for IT leaders and business decision-makers to understand where each platform fits.
– Is Microsoft Purview an endpoint security tool?
– Is Microsoft Defender a SIEM?
– Do you need Microsoft Sentinel if you already have Microsoft Defender?
– And where does data protection fit into the overall security strategy?
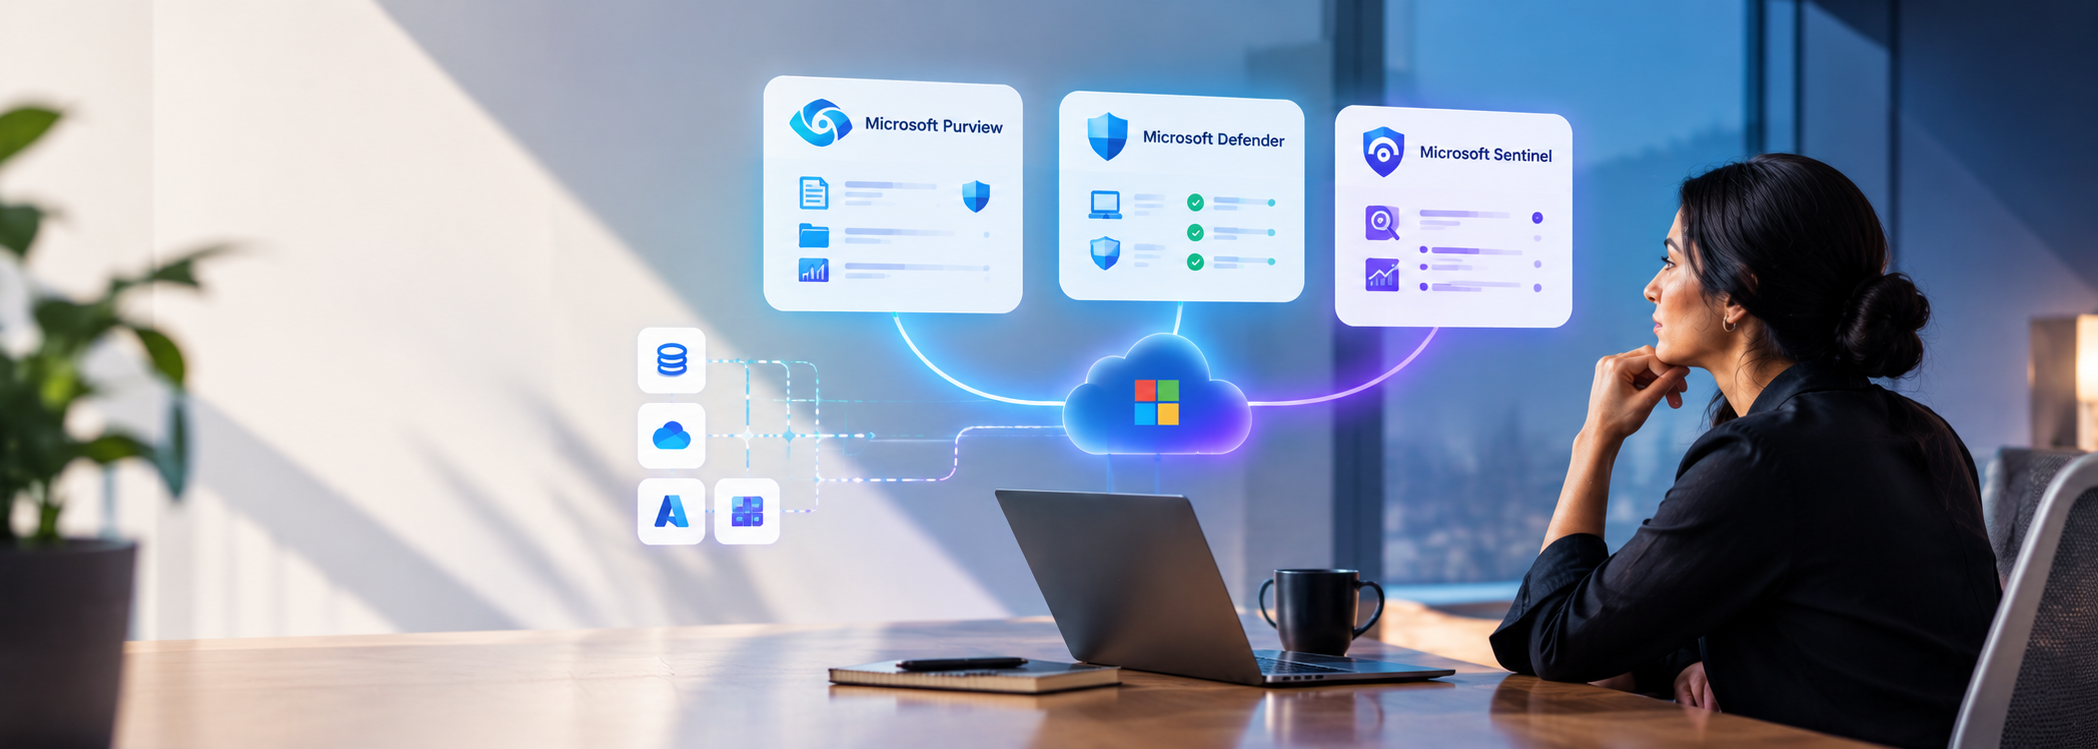
The simplest way to understand the difference is this: Microsoft Purview focuses on your data. Microsoft Defender focuses on threats and attacks. Microsoft Sentinel focuses on security monitoring, investigation, and response across your wider environment.
These platforms can work together, rather than being alternatives to one another. Microsoft specifically describes Defender XDR and Sentinel as complementary technologies, with Defender providing extended detection and response and Sentinel providing SIEM capabilities.
Understanding these differences can help organisations build a more structured Microsoft security environment and avoid treating every security challenge as the same problem.
Microsoft Purview: Protecting and Governing Your Data
Think about the information your organisation handles every day.
– Customer Information
– Financial Records
– Contracts
– Employee Information
– Business reports
– Intellectual property
– Emails and documents
The first security question is not necessarily, “Is someone attacking us?”
It can be: “What sensitive data do we have, where is it located, and who should be able to access or share it?”
This is where Microsoft Purview comes into the picture.
Microsoft Purview provides data security and information protection capabilities that help organisations discover, classify, protect, and govern sensitive information across different environments.
What does Microsoft Purview do?
Purview can help organisations understand their data and apply appropriate controls around it.
For example, an organisation may have sensitive information stored across:
– Microsoft SharePoint
– OneDrive
– Microsoft Teams
– Exchange Online
– End-user devices
– Cloud applications
– Other data sources
Without appropriate classification and protection, sensitive information can easily be copied, shared, downloaded, or sent to the wrong person.
Purview provides capabilities such as sensitivity labels, Data Loss Prevention (DLP), information protection, data security posture management, and insider risk management to help organisations address these challenges.
For example, sensitivity labels can help identify information based on its level of sensitivity and apply protection policies accordingly.
DLP can help organisations identify and control activities involving sensitive information.
This makes Purview particularly relevant when the business question is: “How do we protect our information and control how sensitive data is used?”
A simple way to think about Purview
Data → Discover → Classify → Protect → Govern
Purview is therefore less about identifying whether a laptop has malware and more about understanding and protecting the information that matters to the business.
Microsoft Defender: Protecting Against Threats
Now consider a different scenario. An employee receives a suspicious email. They click a malicious link. Their credentials are compromised. The attacker attempts to access another application. Suspicious activity begins appearing across the environment. This is where Microsoft Defender becomes important.
Microsoft Defender XDR is designed to provide extended detection and response across areas such as endpoints, email, applications, and identities. It automatically collects, correlates, and analyses security signals to help security teams detect and respond to threats.
Instead of looking at every security alert separately, Defender XDR can connect related signals and provide a broader view of an incident.
What does Microsoft Defender protect?
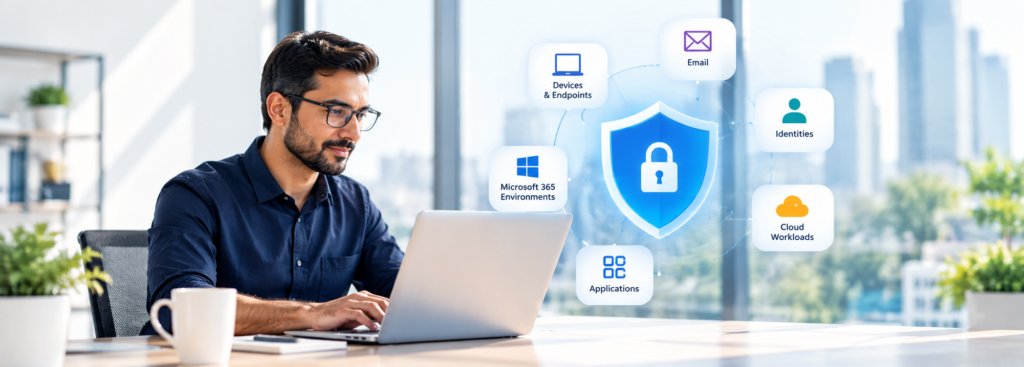
The Defender ecosystem includes different security capabilities for different parts of the environment.
Depending on the Microsoft Defender services deployed and licensed in the environment, protection can extend across:
– Endpoints and devices
– Identities
– Cloud applications
– Microsoft 365 environments
– Cloud workloads
For example, Microsoft Defender for Endpoint focuses on endpoint security, while Microsoft Defender XDR brings signals from multiple security domains together.
The objective is to move beyond simply detecting individual alerts. Instead, security teams can investigate how different signals may be connected.
Why does this matter?
Imagine an organisation receives five separate alerts:
– A suspicious login
– An unusual email
– A potentially compromised endpoint
– A suspicious PowerShell activity
– An attempt to access a business application
Looking at these individually could make them appear unrelated. But when they are correlated, they may represent different stages of the same attack. That broader context is one of the key ideas behind Extended Detection and Response, or XDR.
Microsoft describes Defender XDR as an XDR solution that correlates security signals across Microsoft 365 services and can help security teams investigate and respond to threats.
A simple way to think about Defender
Threat → Detection → Investigation → Response
If the question is: “Are our users, devices, applications, or identities being targeted by a threat?”
Microsoft Defender is a major part of the answer.
Microsoft Sentinel: Seeing the Bigger Security Picture
Now imagine that your organisation has more than just Microsoft 365.
Perhaps you also use:
– Azure
– Firewalls
– Network appliances
– Business applications
– Third-party cloud platforms
– SaaS applications
– Infrastructure from different vendors
– Security tools from multiple providers
Your security team now has information coming from many different places.
This creates another challenge: How do you bring those signals together and understand what is actually happening across the environment?
This is where Microsoft Sentinel fits.
Microsoft Sentinel is Microsoft’s cloud-native Security Information and Event Management (SIEM) platform. It can collect security information from different sources, correlate signals, support investigation, and help organisations respond to threats. It also supports multicloud and multiplatform environments.
Microsoft Sentinel is also transitioning fully to the Microsoft Defender portal, with the Azure portal experience scheduled to retire on 31 March 2027. Organisations still managing Sentinel through the Azure portal should plan their migration to ensure a smooth transition.
How Microsoft Purview, Defender and Sentinel Work Together
This is where the conversation becomes more interesting.
A modern security strategy is rarely about deploying one tool and expecting it to solve every security problem.
Instead, different security capabilities can work together.
Consider a simple example.
Step 1: Sensitive information is identified
An organisation uses Microsoft Purview to identify and classify sensitive information.
For example, certain documents may contain financial or personal information.
Policies can then be applied to help protect that information.
Step 2: A suspicious activity occurs
An employee’s credentials are compromised.
The attacker attempts to access business resources.
Microsoft Defender can detect suspicious activity across relevant identities, endpoints, email, and applications.
Step 3: Security signals are correlated
Other suspicious activity is detected in the environment.
Microsoft Sentinel can collect security data from Microsoft and non-Microsoft sources, helping security teams monitor and investigate activity across the wider environment. In the Microsoft Defender portal, Sentinel is integrated into a unified security operations experience, where Sentinel and Defender capabilities work together through shared incident management.
When Microsoft Sentinel is onboarded to the Defender portal, its incidents are managed through the Defender portal’s unified incident experience. Alerts from Sentinel can be correlated with Defender signals, allowing related activity to be together for investigation.
The result is a more connected security approach:
Purview → Discover, classify, protect and govern data
Defender → Detect, investigate and respond to threats
Sentinel → Collect, analyse and orchestrate security operations across the environment
This is why organisations should not necessarily ask, “Which one should we choose?”
A more useful question can be: “Which security problems do we need to address, and how should these capabilities work together?”
A Real-World Example
Consider a company with 500 employees using Microsoft 365, Azure, laptops, SaaS applications, and a mixture of cloud and on-premises systems.
The company has three different challenges.
Challenge 1: Sensitive documents are being shared externally
Employees regularly share documents through Teams, SharePoint and email.
The IT team is concerned about sensitive business information leaving the organisation.
This is primarily a data security and information protection challenge.
Microsoft Purview can be relevant here.
The organisation can use capabilities such as classification, sensitivity labels and DLP policies to help identify and protect sensitive information.
Challenge 2: Employees are receiving sophisticated phishing emails
One employee clicks a malicious link.
An endpoint begins showing suspicious behaviour.
The user’s identity also shows unusual activity.
This becomes a threat detection and response challenge.
Microsoft Defender XDR can bring together signals from relevant security services and help security teams investigate the incident.
Challenge 3: Security information is spread across multiple platforms
The organisation also has firewall logs, Azure activity, third-party applications and other infrastructure generating security events.
The security team needs a centralised way to analyse these signals.
This is where Microsoft Sentinel can provide SIEM capabilities and broader security visibility.
The three technologies therefore address different parts of the same overall security strategy.
Why the Difference Matters for IT Leaders
For IT leaders, understanding these distinctions is not just about knowing Microsoft’s product portfolio.
It is about making sure security investments address actual business risks.
An organisation may have strong endpoint protection but limited visibility into sensitive data.
Another may have good data classification but limited centralised security monitoring.
Another may have multiple security tools but no effective way to correlate the information they generate.
Security maturity is therefore not simply about having more tools.
It is about whether the tools work together to address the organisation’s actual risks.
Microsoft’s guidance highlights the complementary relationship between Defender XDR and Sentinel, including their integration for unified security operations.
The same principle applies when considering data protection.
Security teams need visibility into both what attackers are doing and what information they could potentially access or compromise.
Final Thoughts
Microsoft Purview, Microsoft Defender and Microsoft Sentinel are often discussed together because they can contribute to a connected Microsoft security environment. But their primary purposes are different.
Purview is centred around data security and information protection.
Defender is centred around threat detection, investigation and response.
Sentinel is centred around SIEM capabilities and broader security monitoring.
The goal should not simply be to deploy all three because they are available within the Microsoft ecosystem. Instead, organisations should first understand their security priorities and then determine where each technology fits.
Mismo Systems is a Microsoft Solutions Partner for Security, helping organisations strengthen their security posture across Microsoft 365, cloud, identity, endpoints, and data. With expertise across Microsoft Purview, Microsoft Defender, Microsoft Sentinel, Entra ID, Intune, and Microsoft 365 security, we help businesses build practical and connected security environments aligned with their needs.
For some organisations, the immediate priority may be understanding and protecting sensitive data.
For others, it may be strengthening endpoint and identity threat protection.
For organisations with complex environments, centralised security monitoring and SIEM capabilities may be a major requirement.
And in many environments, these needs overlap. That is where the combination becomes valuable.
Purview helps answer: “What data are we protecting?”
Defender helps answer: “What threats are we facing?”
Sentinel helps answer: “What is happening across our security environment?”
Understanding these three questions is a useful starting point for building a more structured, connected and business-focused Microsoft security strategy.
If you’re unsure where to start, request a Free Microsoft 365 Security Assessment or Contact Our Security Experts
FAQs
Microsoft Purview focuses on data security, information protection, governance, and compliance. Microsoft Defender focuses on detecting, investigating, and responding to threats across endpoints, identities, email, and applications. Microsoft Sentinel is a cloud-native SIEM that provides broader security monitoring, correlation, investigation, and response across an organisation’s environment.
Yes. These solutions address different areas of security and can work together as part of a broader Microsoft security strategy. Purview helps protect sensitive data, Defender helps detect and respond to threats, while Sentinel can bring security signals together for broader monitoring and investigation.
No. Microsoft Sentinel is primarily a SIEM platform designed for security monitoring and analysis across different environments. Microsoft Defender XDR focuses on extended detection and response across areas such as endpoints, identities, email, and applications. They can be integrated to support a more connected security operations approach.
Microsoft Purview is particularly relevant when an organisation needs better visibility and control over sensitive information. Common use cases include data discovery and classification, sensitivity labels, Data Loss Prevention (DLP), information protection, and compliance requirements.
Not necessarily. The right combination depends on the organisation’s security requirements, existing Microsoft environment, risks, compliance needs, and security maturity. Organisations should first identify their key security challenges and then determine which capabilities are required to address them.